I don’t know how.. If someone can help. I get this message: Also saw someone with an executor if you guys can be detectives and find out where it’s coming from. I managed to patch the cuffs.


1 Like
Search in your scripts if you have “getfenv” or “require(”
If you see it delete it
You’re actually the goat!! Thank you. Is there anything else you want to add or say?
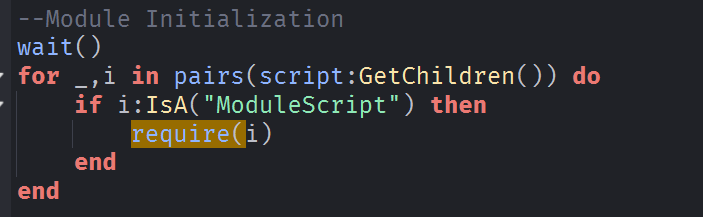
Your game most likely has a backdoor, often introduced through an infected Toolbox asset.
I’d recommend using Ctrl + Shift + F and searching for suspicious patterns such as:
require(— especially if it requires an unfamiliar asset IDloadstring(HttpGetGetAsyncPostAsyncHttpServiceInsertServiceLoadAssetInsertGetObjectsScript.SourceCoreGuiRemoteEvent/RemoteFunctionbeing created or accessed unexpectedly- Obfuscated code using lots of
string.char,string.reverse,string.gsub, etc. - Scripts containing very long/random-looking strings or encoded data
game:GetService("InsertService")game:GetObjects(...)require(<random/unknown asset ID>)
Important: don’t delete every script containing require() or HttpService automatically. Legitimate systems can use these too. Check whether the script is something you intentionally installed and where it came from.
You can also search the Explorer for c:script to see the scripts in your place and inspect anything you don’t recognize.
AI can help analyze suspicious scripts, but always manually review its findings and test the game afterward. Backdoors can also hide themselves across multiple scripts, so removing one suspicious script isn’t always enough.
By any chance have you added anything in the game from Toolbox that contains Scripts? It can be anything; Models, Admin Panels etc..
1 Like
The only free models I use is Adonis Admin, but it was probably my other devs and/or contributors that added this, but I am deep searching every script.
And I definitely want to patch those exploits if I ever see my own game on a some scripts website off of Roblox.
It might be Adonis Admin then, I suggest you try to delete the current one that’s in your game and re-installing it from the original package.
Alright, thank you. I will definitely keep an eye on new backdoors. Appreciate your help.
1 Like
there are several unpatched exploits that let people just shutdown any server as you say
this is regardless if you have perfect code and no possible backdoors or anything like exposed remoteevents
1 Like
Do you know where the several unpatched exploits are coming from and/or how it works?
This topic was automatically closed 14 days after the last reply. New replies are no longer allowed.