I tried to do but without loadstringenabled its impossible for me…
This won’t work.
CoreGui cannot be accessed from any security contexts that we as developers have access to.
game:GetService("CoreGui")
will return nil
Even putting that aside, basing a whitelist off of instance names rather than just referencing the instances directly is stupid.
Additionally, there’s no reason to fire a remote to kick the client. The client can kick itself. Regardless exploiters can prevent remotes from being fired, and can prevent their own client from kicking themselves.
3 Likes
Im not familar with roblox core thing, but wasnt GetService on CoreGui returns nil?
How do you even setmetatable on this
Yes, it does
100% sure everything the guy posted is stolen from a old post or/and is AI generated
- GetService(“CoreGui”) returns nil for game scripts
- I don’t see what this SharedTable code is supposed to accomplish. Either way you can just aswell hook SharedTable.new or SharedTable.clone
1 Like
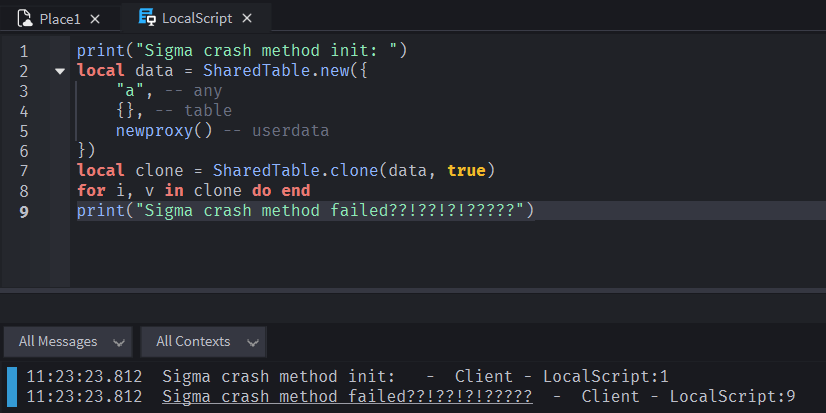
Everything you have said so far is wrong. This is not a crash method, your detection doesn’t work and a client can absolutely prevent a crash.
1 Like

I’m assuming it’s in starterplayerscripts. Try a task.wait perhaps? It worked for me 2 years ago
What are you saying?
None of this worked and will ever work, you just posted things you found online gang it’s really that simple
Theres already a task.wait(5), I’m using your code with a print at the end. What are you hoping this accomplishes anyways? Do you think just because something is in StarterPlayerScripts it will magically skip over code straight to the print?
If any of you have any suggestions for helping out OP I’d list them, I’m purging my posts for this page. I promise you that it genuinely worked 2 years ago. Perhaps it was patched. I’m old now..
A better suggestion would be 1 simple rule, never trust the client. Implement proper server side validation. There are many ways to detect flying and other movement cheats. I’ve made community tutorials on website hosted json databases you can source your banned users to for use across multiple games if anyone needs it.
Instead of trying to detect specific scripts, it’s usually better to just handle important logic on the server and validate. Any data received from the client should be entirely untrusted.
2 Likes
The cool thing is that people can then make cheats like ESP, or some other crap, or even use SaveInstance() to copy the map and see what’s in the game, so I’m doing both at the same time, and I’m specifically writing Decompiler Failed Please Try Again in the module scripts so that the cheaters will think about why the module isn’t loading, and after 100 lines, I’m writing the script itself
2 Likes
writing Decompiler failed please try again in script is a good idea and might work for expoliter xD
1 Like
i may be mistaken with this info, but im pretty sure that dex does not properly cloneref instances it references. This means you can put certain instances which should never be referenced into a weak table and check whether or not they get collected. This was particularly useful on CoreGui until the security level was changed, but it should still work on other instances.
don’t use remotes either, use some kind of crashing method.
I’ve attempted to delete the posts i made correcting my mistakes because others on here didn’t agree with my methods. I used to use a crash table method. That doesn’t work anymore.
There are plenty of available anticheats on here.
You do realize the decompiler output will not include whitespaces from your script right?
And you do realize theres no way to detect or prevent proper saveinstance right?
And you do realize there’s no way to detect proper ESP right? Do it like PF, make a good votekicking system.
This must be a joke. You don’t write anti-cheat in a local script, you can very easily destroy it without Dex (And checking it can also be destroyed.). Everything that is client sided is what a script injector has access to.
Then again, the average Dex & Infinite Yield user is also running malware, so we can’t assume they know anything about anything. But for that edge case where they do know what they’re doing, just use a part instanced on the server to create a forever hitbox, which can be checked effectively.
Some resources for patching exploits:
1 Like
This is one of the big suggestions I’ve seen when researching physics-based exploits (They’re pointless to patch, Nobody uses them in competitive games.) Always implement a vote-kick system if you believe it’s necessary.
A vote kick system is preposterous to implement into your game. You don’t think it won’t get taken advantage of at some point? I’m certain there is at least some vulnerability.
I have physics based exploit detection in my own game to monitor player behavior. It’s easy to bypass of course but just don’t give up.
Anti exploit is all in vain. The only way in my personal opinion is to set up something to monitor a player and see actual signs of exploiting. Such as earning in game currency too fast, those client logs are then sent to some sort of portal you can review and put their user ID into an online database manually. I’ve wrote posts on how to do it. There is no fool proof system.
The goal is to make it difficult enough to make it useless. Also turn off player collisions to if need be. You can also scan for rapid rotation of a player for fling exploits. Tool exploits too. Easily detectable. Also set up bait remote events for remote event fire programs.