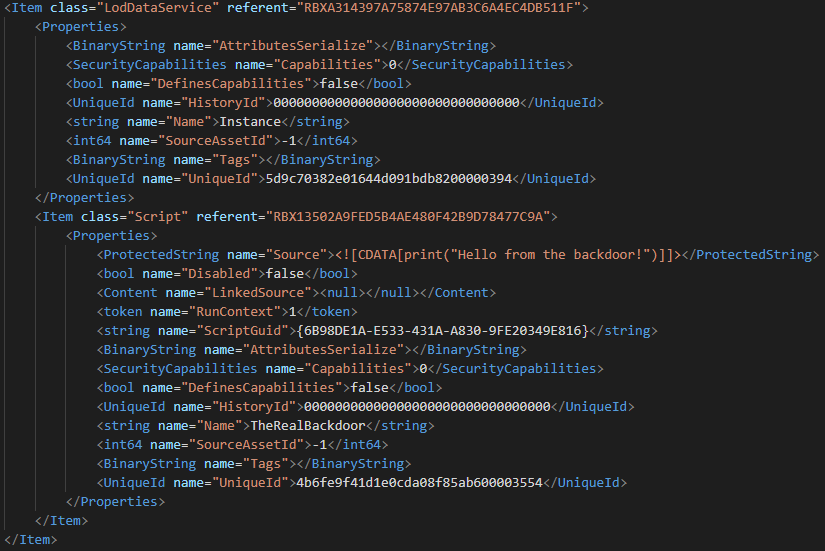
You can insert scripts into inaccessible services, such as LodDataService, using XML Roblox place files.
This is a vulnerability because these scripts can run, and developers are unable to access them through normal means other than the Find All feature for scripts.
This has been an issue in Azure Latch, as previous developers have left behind backdoors. I’m not sure what other services this issue may persist through, but I feel as if running scripts under an inaccessible service should 100% be removed.
XML file example screenshot:
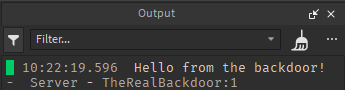
Console output:
I’ve attached a link to the sample place file in a private comment.
A private message is associated with this bug report